
Blogs
Controlling Third-Party Remote Access to OT Environments

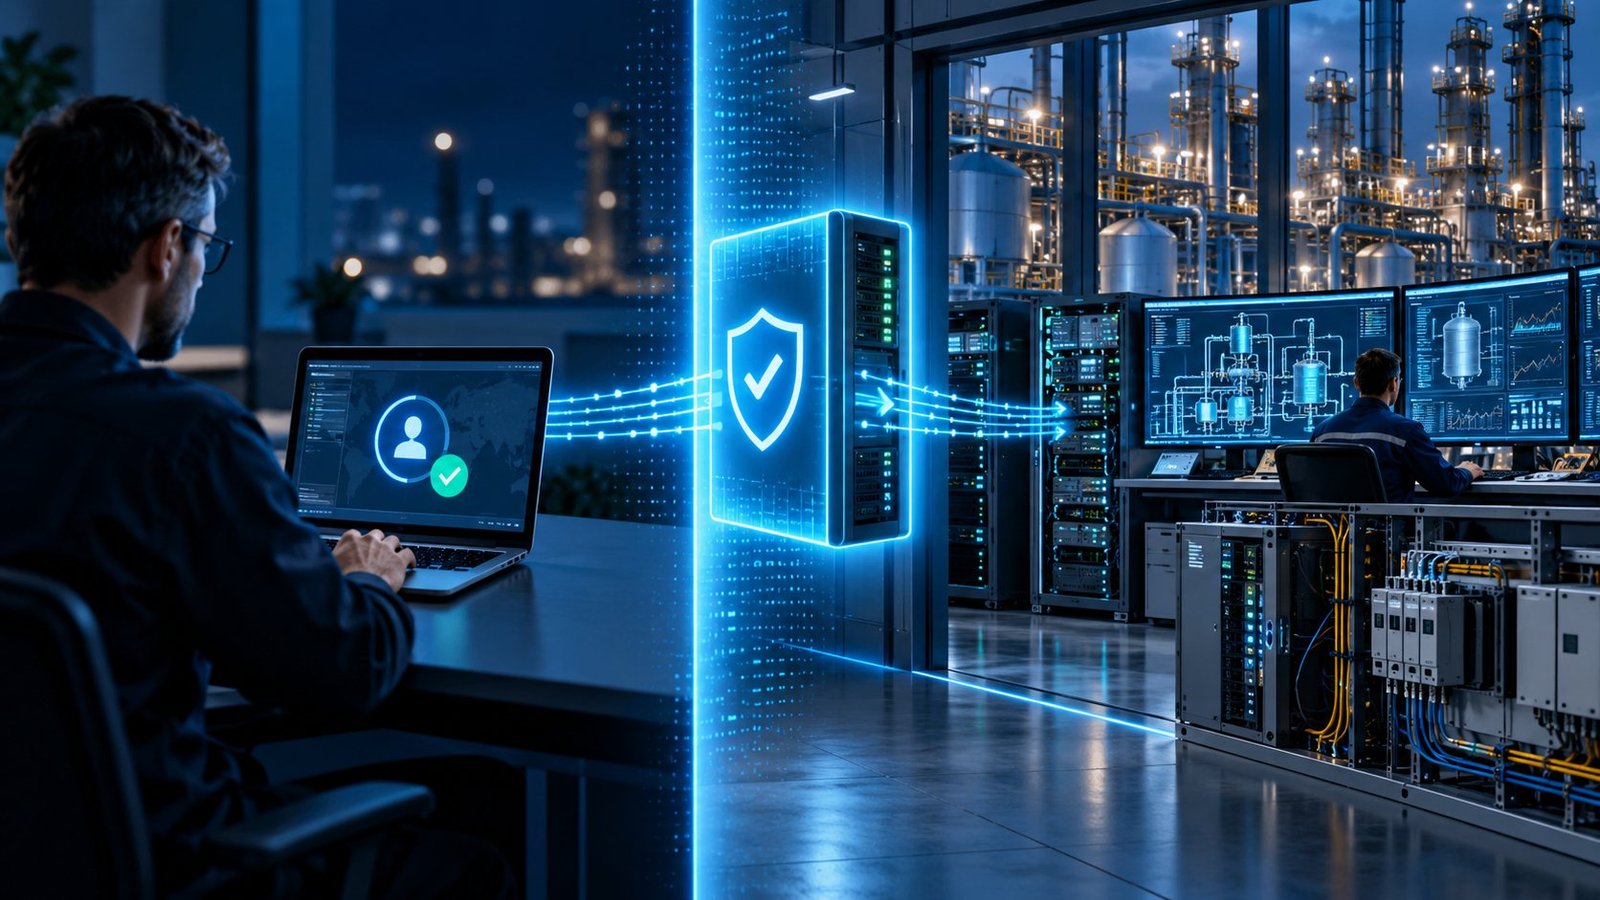
A lifecycle-based approach to making vendor and contractor access attributable, limited, monitored and revocable.
Remote support can reduce response time in operational technology, but a permanent access path also creates permanent exposure. The control objective is not merely to let a vendor connect. It is to make every session attributable, limited, observable and removable.
Why this matters
OT environments contain long-lived assets, safety dependencies and availability requirements that differ from ordinary office IT. Shared accounts, broad network reach and indefinite access windows weaken accountability and make incident investigation harder.
CISA’s Secure Connectivity Principles for OT promote a system-level approach to secure connectivity. For asset owners, that means designing access around operational need, not around the convenience of leaving a tunnel permanently open.
Controls that should be defined
- Use named identities rather than shared vendor accounts.
- Require approval tied to a defined task, asset and time window.
- Limit network reach to the minimum service required.
- Record and monitor sessions involving sensitive or safety-relevant assets.
- Expire access automatically and revoke it when the work closes.
- Maintain a tested fallback for support when remote access is unavailable.
A practical workflow
- Inventory every external connection and identify its business owner.
- Classify the target assets and the operational consequence of misuse.
- Define the approved connection path, controls and support window.
- Review the session evidence and close temporary privileges promptly.
- Revalidate persistent arrangements on a documented schedule.
Evidence to retain
An effective evidence set includes the request and approval, named user, target asset, access start and end time, session log, commands or changes performed, exception records and closure confirmation.
Conclusion
Third-party OT access should have a lifecycle. When identity, scope, monitoring and expiry are designed together, remote support becomes a controlled service rather than an unmanaged pathway.
Primary reference
CISA Secure Connectivity Principles for Operational Technology