
Blogs
Controlling Third-Party Remote Access to OT Environments

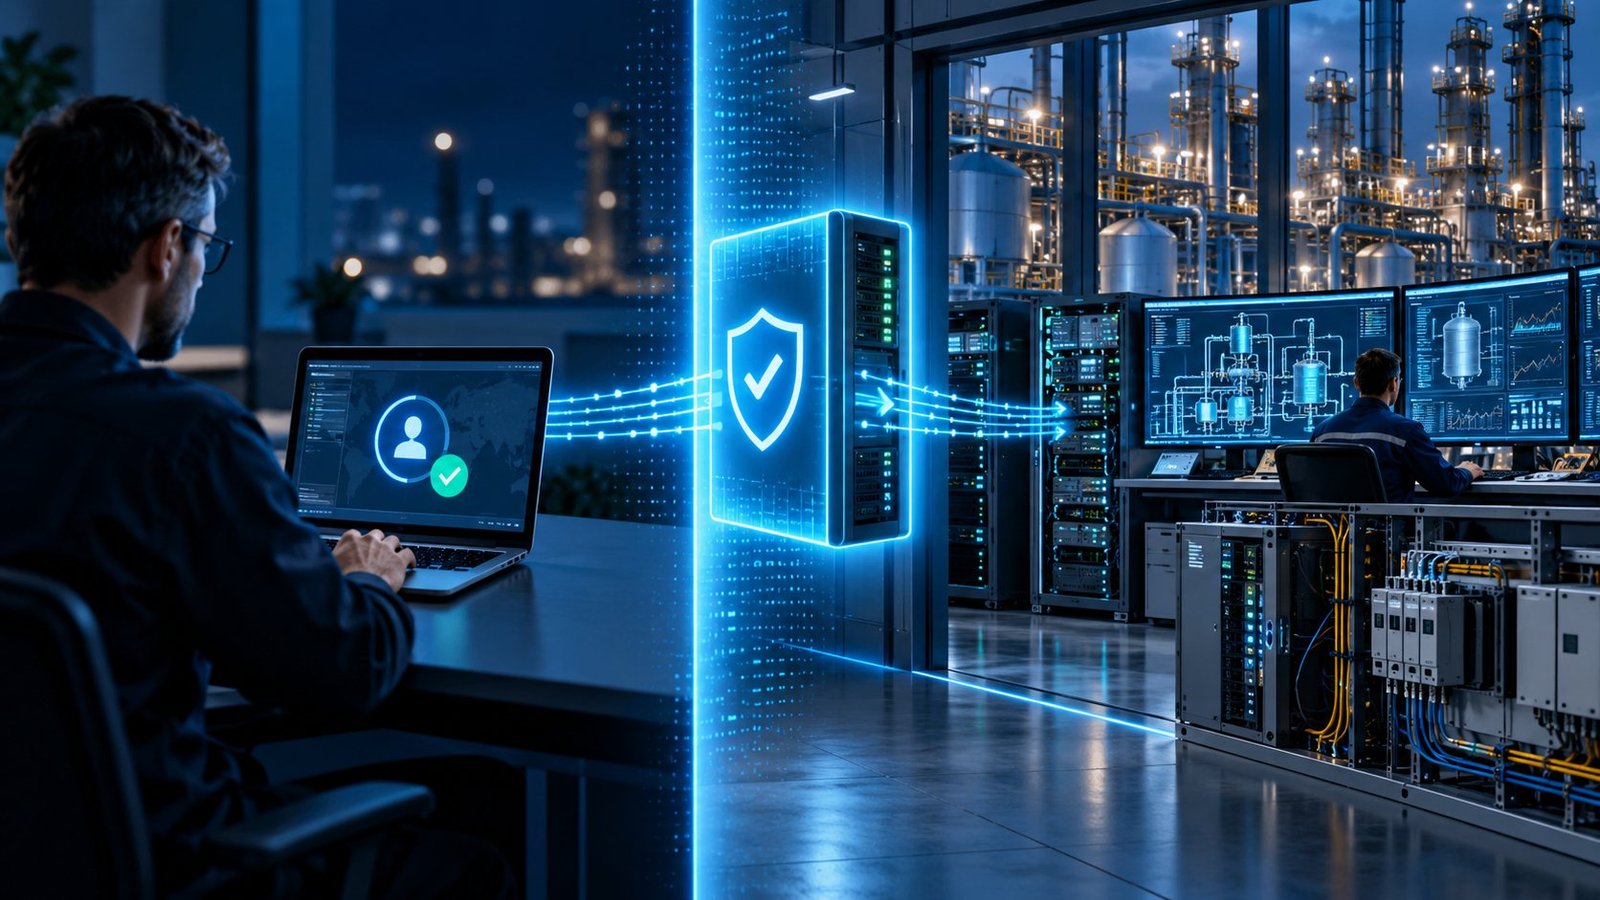
Summary: Vendor access to operational technology should be designed around the task and the consequences of misuse, not around the convenience of a permanently open connection.
What the joint guidance says
The Secure Connectivity Principles for Operational Technology were developed by the UK National Cyber Security Centre with international partners, including ASD’s ACSC and CISA. They call for risk-informed connectivity, reduced exposure, controlled access, monitoring and an isolation plan that protects operational continuity.
CNB Telecom’s applied checklist
- Identify the owner, purpose and target assets of each external connection.
- Use individual identities and task-specific, time-limited permissions.
- Route remote access through an approved, centrally managed path rather than separate uncontrolled vendor tunnels.
- Monitor relevant sessions and retain approval and activity records.
- Remove temporary privileges when work ends and test how support and operations continue without the connection.
This is an implementation checklist informed by the guidance, not a substitute for a site-specific safety and security assessment.
Original source
Independently summarized and reviewed by CNB Telecom
Last reviewed: October 10, 2026.